Skip to content
Built for Zambian corporations, pension funds, insurers and regulated institutions

Internal audit and risk management, automated. Scored from your own risk register.

Run the IIA audit cycle and ISO 31000 risk process on one platform

Ontech Audit & Risk ranks your audit universe from the live risk register, builds the annual plan within your capacity, runs engagements with versioned workpapers and full-population analytics, chases every agreed action up an escalation ladder, watches your systems continuously, and produces the Audit Committee pack in PDF, Word and PowerPoint. Your auditors judge; the platform does the chasing.

Risk-scored audit universe 8 full-population tests Four-level escalation ladder Committee pack in 4 formats
8
Standard audit programmes
8
Analytics tests on whole populations
4
Escalation levels, owner to committee
4
Report formats: PDF, Word, PowerPoint, Excel
1
Database for audit and risk
Connected to real data

Every figure comes from a real source

The audit plan is scored from the risk register, the analytics run on your own ledgers, and the monitors query your systems. Nothing on the dashboard is typed in.

The risk register

Every auditable entity is linked to the risks it carries. Their residual scores drive half of its audit priority, so the plan follows the register, not last year's plan.

  • Re-scored every time the universe opens
  • Findings link back to the risk and the control they test
priority = 50% register risk + 30% inherent rating + 20% time since last audit

Your ledgers and extracts

Payments, journals, payroll, loan books and user lists, uploaded as CSV or Excel. Each file is fingerprinted with SHA-256 and profiled column by column before any test runs.

  • The population tested is the evidence on file
  • Results file straight into the workpapers
CSV · Excel

Live system connections

Read-only queries against your ERP, payroll or core system, on connections your ICT team controls. The platform never stores the credentials and only ever runs SELECT.

  • Row caps and time-outs on every query
  • Password hashes and secrets are refused and stripped
Read-only

Key risk indicators

Thresholds and tolerances per indicator, measurements captured by hand, by import or from a connection, and a breach that alerts the owner and shows on the dashboard.

Early warning

Incidents and losses

Incidents, losses and near misses with root cause and corrective actions, linked to the risk they realised and watched by the same monitors as everything else.

Root cause

Evidence that proves itself

Every workpaper version keeps its SHA-256 fingerprint, uploader and time; a different person must review it; and every status change is on the engagement's trail.

Tamper-evident
Who it’s for

One platform for everyone in the three lines

Each role sees its own work; the Audit Committee sees the whole picture.

Chief Audit Executive

The committee pack assembled by hand from spreadsheets the week before the meeting

With Audit & Risk: approve the plan on screen, watch delivery against the year, and generate the pack from live data in PDF, Word or PowerPoint

Approves · reports

Auditors

Samples of 25 because the full ledger would take a week in Excel

With Audit & Risk: test the whole population in minutes, file the result as a workpaper, raise the finding in one click, and log the time against the step

My Audit Work

Risk officers and champions

Treatment actions that drift past their dates with nobody chasing

With Audit & Risk: one register, KRIs with alerts, and the same escalation ladder for treatments as for audit actions

ISO 31000

Auditees and action owners

Reminders by e-mail with no record of what was promised or done

With Audit & Risk: see only your unit's engagements and your own actions, update progress, and close them when audit verifies

Own unit only
Automation

What runs without anyone pressing a button

Six jobs the platform does on its own. People step in only where a judgement is needed.

A universe that ranks itself

Every entity is re-scored from the register whenever the page opens, so the priority order is never stale.

  • Never-audited entities rise to the top
  • Closing an engagement resets the entity's cycle
Live scoring

A plan proposed within capacity

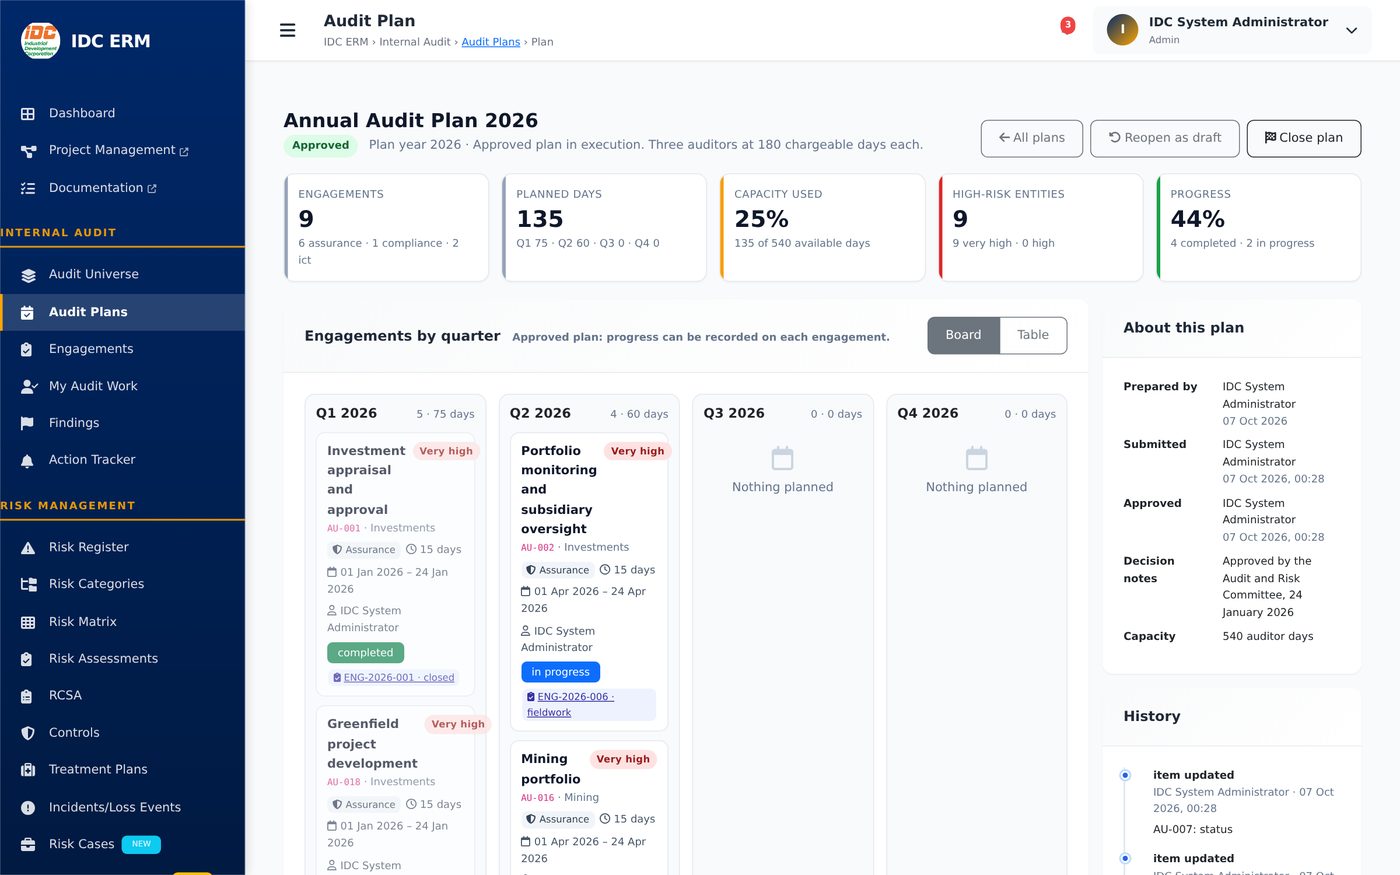
Give it the available auditor days and the minimum band; it proposes the year's engagements in priority order, spread over the quarters.

  • Submit, approve, reject or reopen with notes
  • Board, table and timeline views of the same plan
Risk-based

Follow-up that chases itself

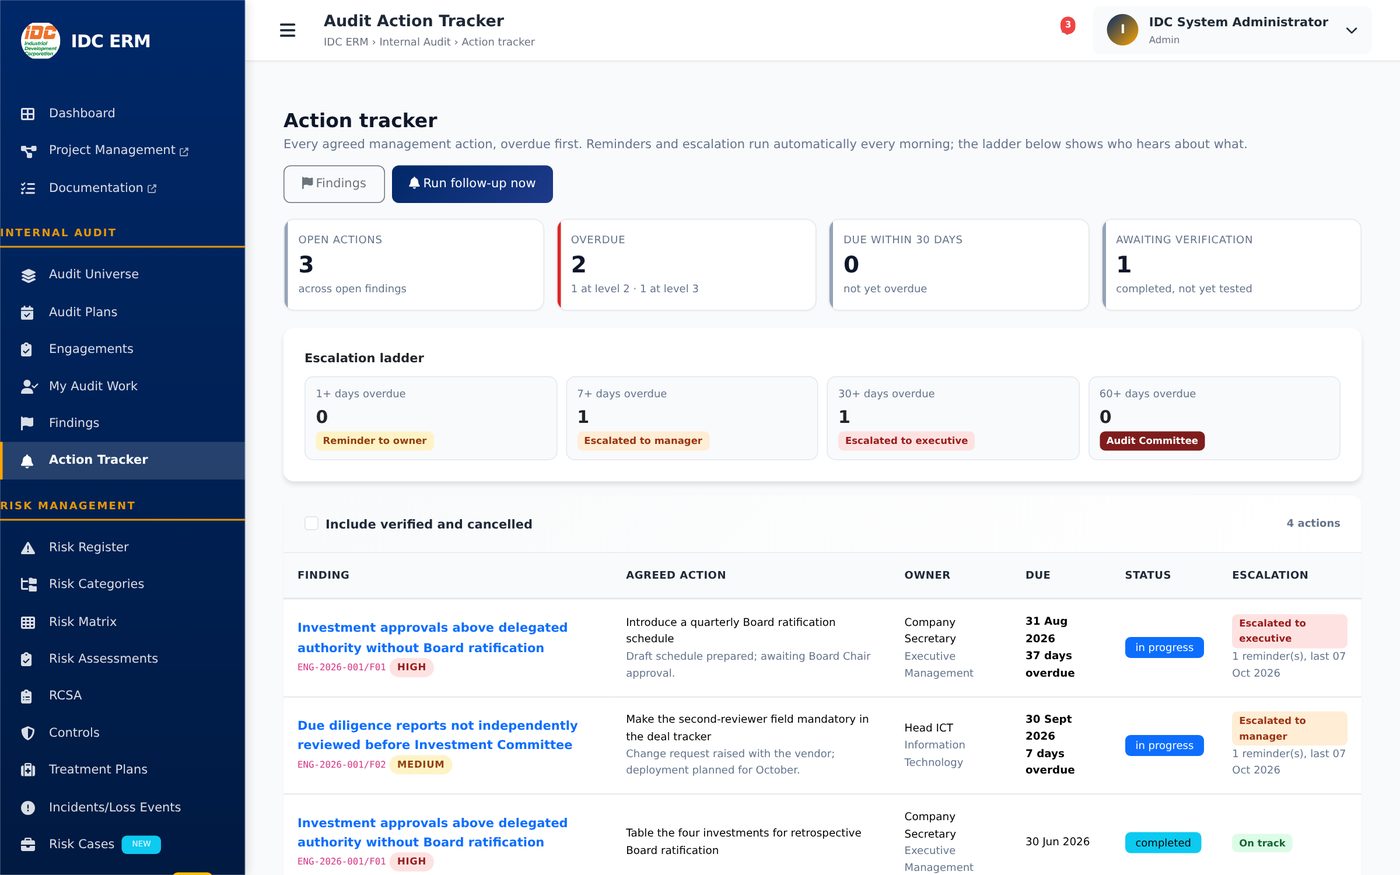
A sweep every morning reminds owners of overdue actions and escalates by age. Each level is logged once; reminders repeat weekly.

1+ daysOwner
7+ daysUnit head
30+ daysExecutive
60+ daysCommittee

Monitors that watch your systems

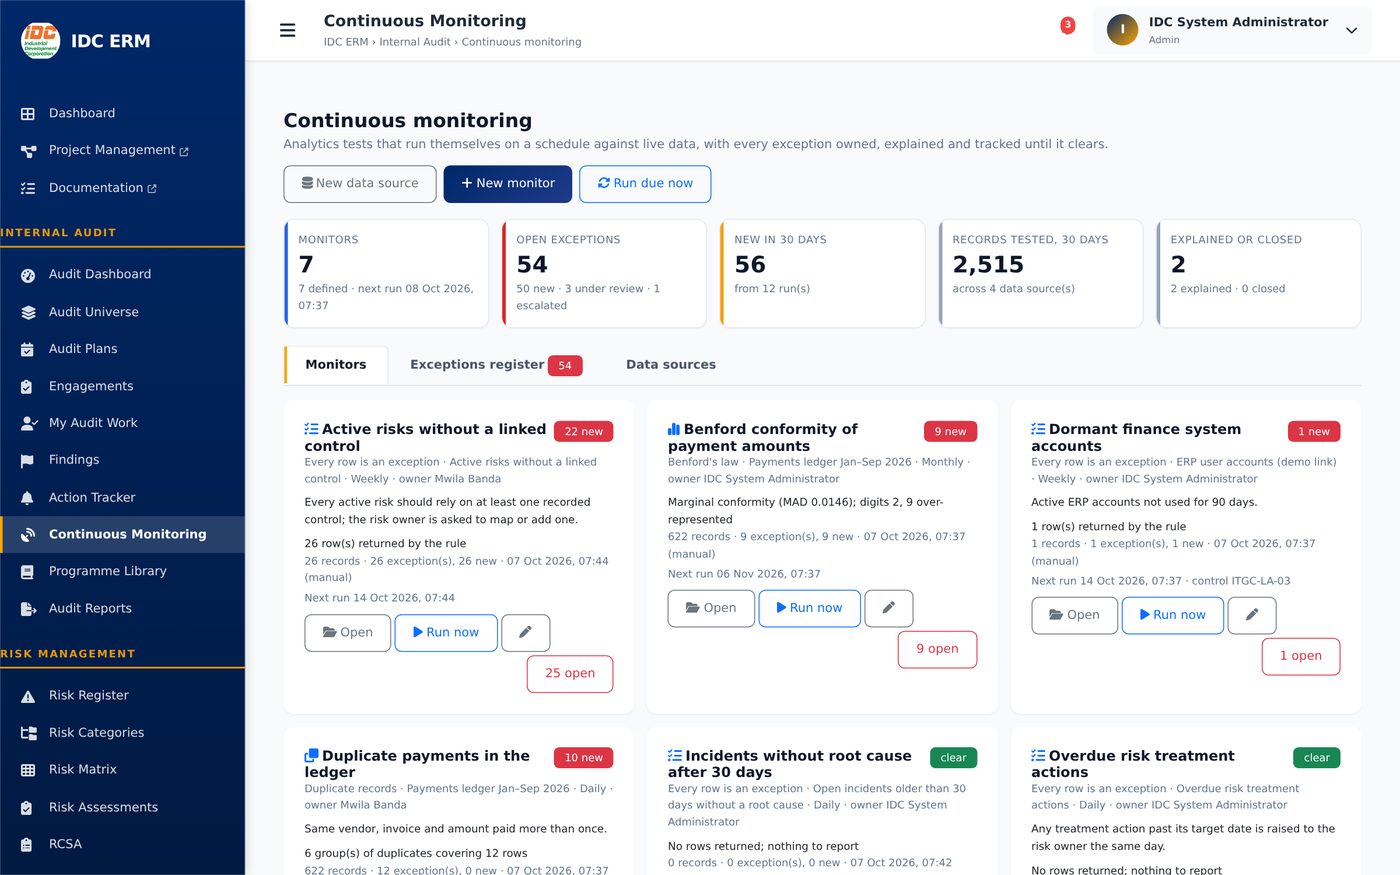
A rule, a data source and a schedule. Every run compares its exceptions with the last: new ones are owned and notified, repeats keep their explanation, cleared ones close themselves.

  • Duplicate payments, unapproved vendors, dormant accounts, overdue treatments
  • Hourly, daily, weekly or monthly
Continuous

Four-eyes the system enforces

A workpaper's reviewer cannot be its preparer. A finding's author cannot review it. A finding cannot close until internal audit has verified every agreed action.

By design

Reports that write themselves

The engagement report, the annual plan and the Audit Committee pack are generated from the data at the moment you ask, and every generation is logged.

  • PDF for the file, Word for the wording, PowerPoint for the meeting, Excel for the analysis
4 formats
Standards

The standards, mapped to what the platform does

The audit cycle follows the IIA Global Internal Audit Standards; the risk process follows ISO 31000.

Risk-based planning

A documented audit universe, a priority method you can explain, and a plan the committee approves on the record.

GIAS 9.4

Engagement documentation

Programmes, versioned workpapers with sign-off, and an activity trail that shows who did what and when.

GIAS 14.6

Findings and communication

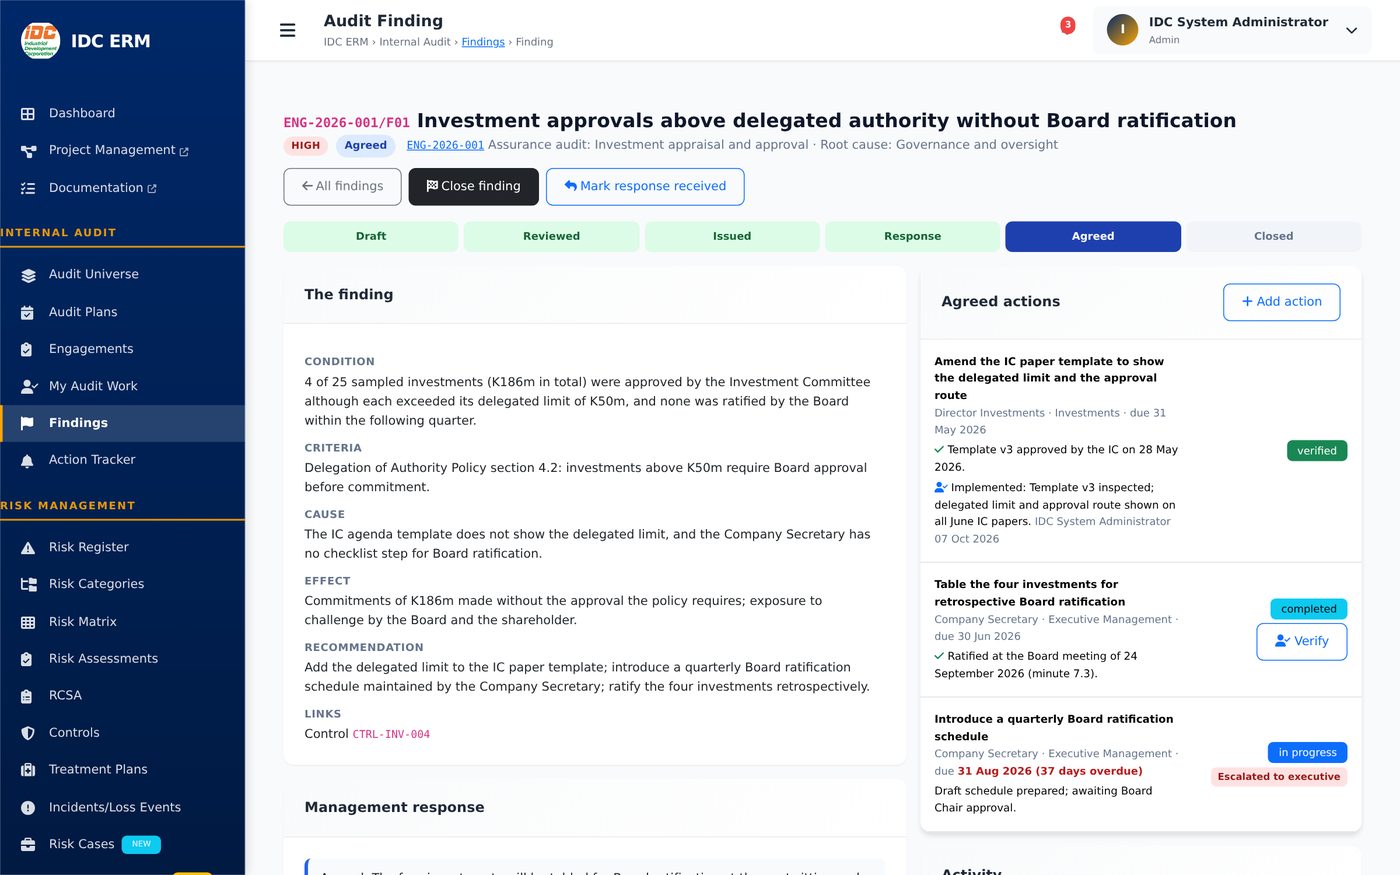
Condition, criteria, cause, effect and recommendation on every finding; management responses and agreed actions on the record.

GIAS 14.3 · 15.1

Monitoring action plans

Automatic follow-up, verification by internal audit, and escalation to the committee for what stays open.

GIAS 15.2

Risk management process

Context, identification, analysis, evaluation, treatment, monitoring and communication, with configurable scales and a matrix.

ISO 31000

Board reporting

Plan delivery, findings by rating and root cause, action ageing, monitoring position and universe coverage in one pack.

Committee-ready
Analytics

Eight tests written for how money moves

Chosen from drop-down lists of the columns in your data. No scripting language, no separate desktop licence.

Duplicate records

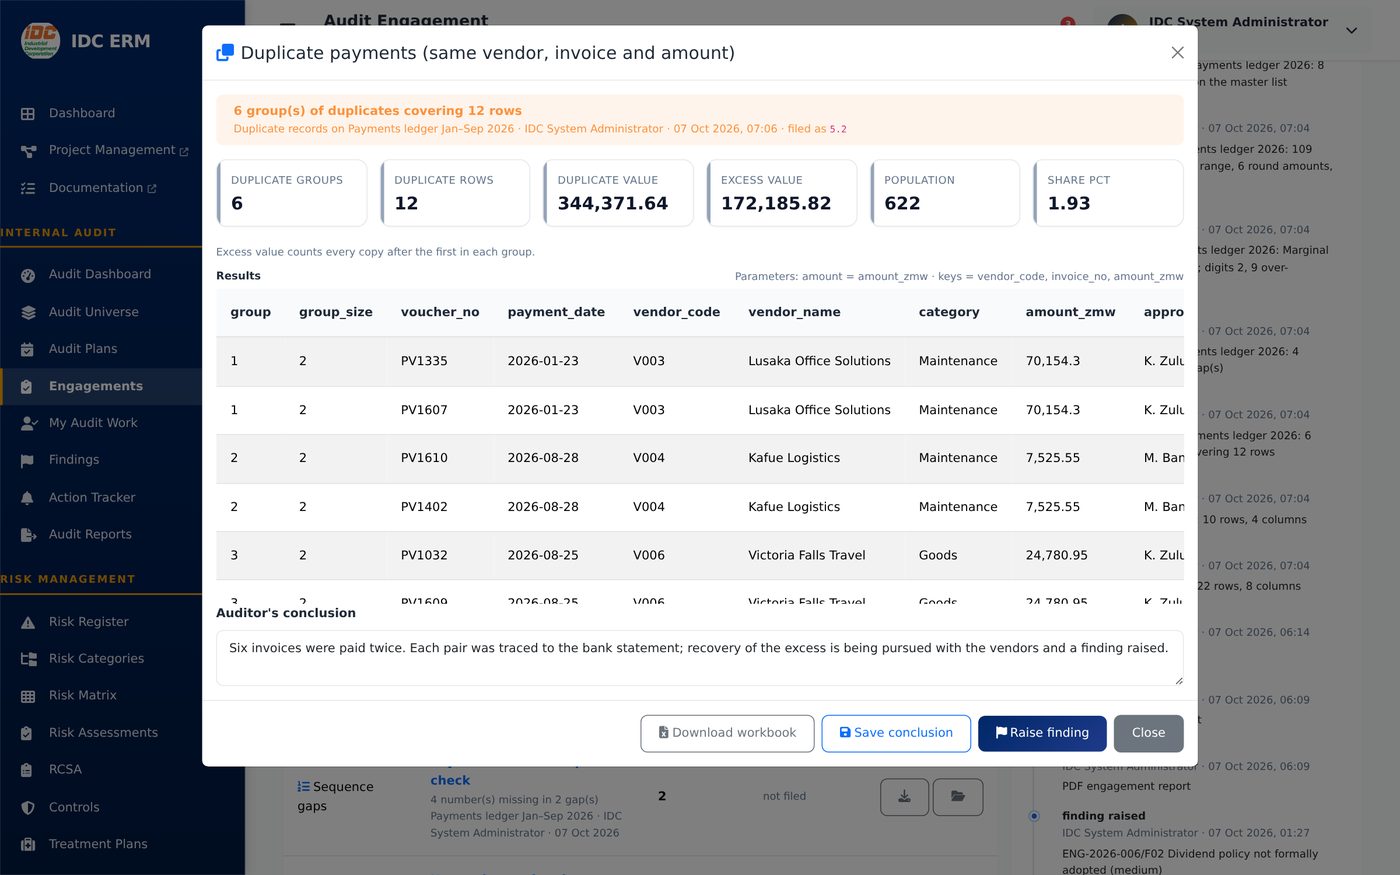
Same vendor, invoice and amount paid twice, with the excess value totalled.

Sequence gaps

Missing and reused voucher, cheque or receipt numbers.

Benford's law

First-digit distribution against expectation, with a conformity verdict.

Unusual values

Amounts outside the normal range, round amounts, weekend postings.

Match to a master list

Payments to suppliers not on the approved vendor master.

Summarise by group

Totals by approver, cost centre or vendor, with each one's share.

Sampling

Random, systematic, monetary-unit or largest-item, with a recorded seed.

Every row is an exception

For queries that already apply the rule, such as overdue treatment actions.

How it works

From the risk register to the Audit Committee

Five steps, the same every engagement, with a record of each one for the reviewer.

1

Plan

The universe is scored from the register; the year's plan is proposed within capacity and approved on screen.

2

Execute

Each engagement loads its programme from the library; the team works the steps and logs its days.

3

Evidence

Workpapers are versioned and signed off by two people; analytics test whole populations and file their results.

4

Report

Findings with the five C's, management responses and agreed actions; the report generated in the format the reader needs.

5

Follow up

Actions chased up the ladder, verified by audit, and the position tabled in the committee pack.

Product tour

See it as your auditors will

Screens from the running system, with sample data.

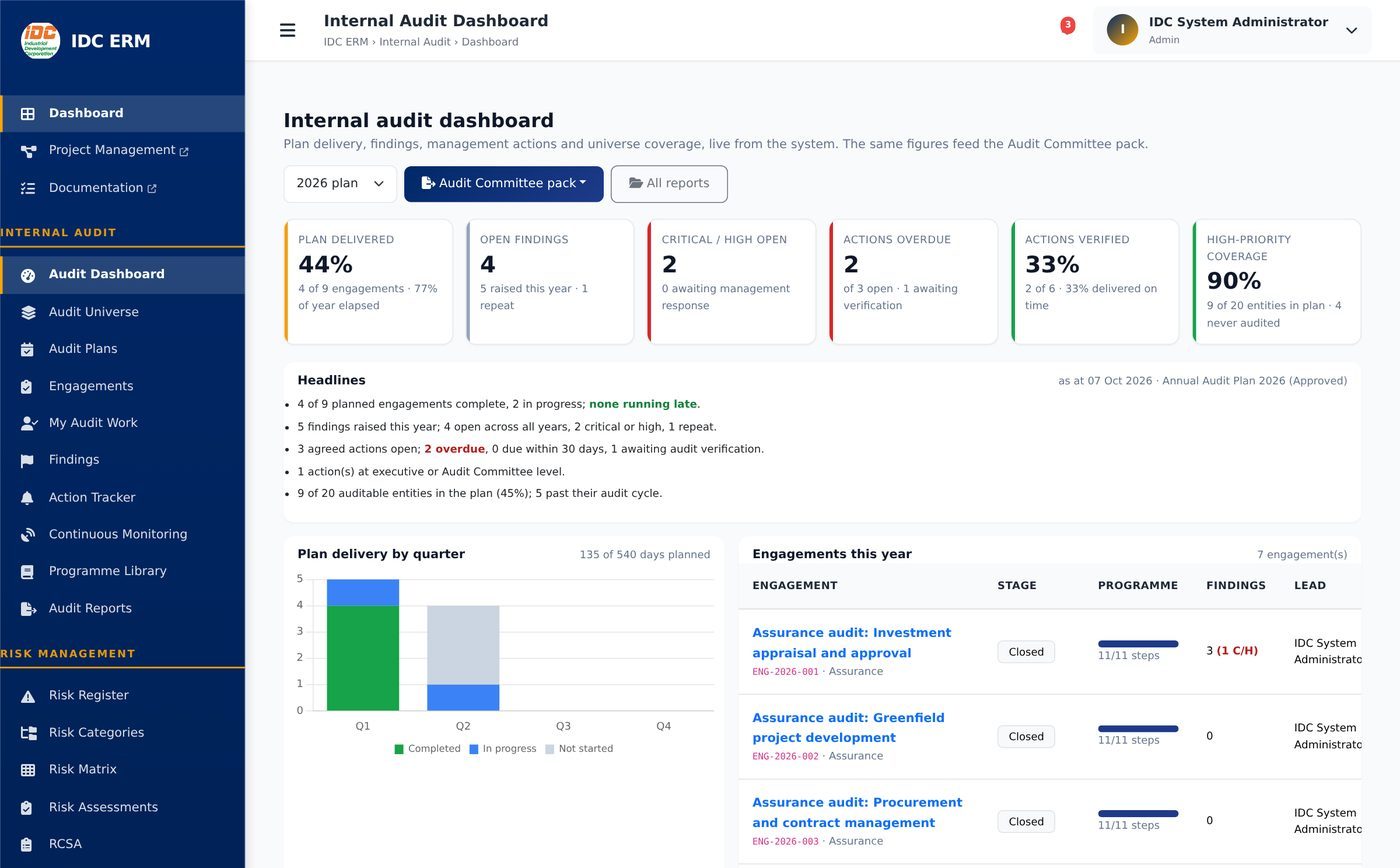
Internal audit dashboard

The Internal Audit dashboard: plan delivery, findings, actions, monitoring and coverage, live.

Analytics results: duplicate payments

A duplicate-payments test on a 622-row ledger, filed as workpaper 5.2 with the auditor's conclusion.

Continuous monitoring

Continuous monitoring: seven monitors, their last results and open exceptions.

A finding with management response and actions

A finding: condition, criteria, cause, effect, recommendation, the management response and its agreed actions.

Action tracker with escalation ladder

The action tracker and its escalation ladder.

An approved annual plan on the quarter board

An approved annual plan on the quarter board, with capacity and coverage.

Security

Secure by default

What protects your evidence and your decisions, switched on from the first day.

Two-step sign-in

A password plus a one-time code by e-mail; Active Directory sign-on where you have it; accounts lock after repeated failures.

Least privilege

Roles for the Chief Audit Executive, audit managers, auditors, auditees and the committee; auditees see only their own unit and actions.

Four-eyes and a full trail

Preparer and reviewer, author and reviewer, owner and verifier are always different people, and every step is logged with who and when.

Evidence integrity

Every uploaded file and dataset carries a SHA-256 fingerprint, so what was tested is what is on file.

Read-only connections

Monitors run SELECT only, with row caps and time-outs; credentials stay with your administrator; secret columns are refused.

Yours to host

Containers on your own servers or a cloud of your choice; the same software either way, operated by Ontech Solutions, a registered data controller.

Contact

Request a demo

We'll walk your audit and risk teams through the platform with your own universe and a sample ledger.

Ready to put audit follow-up on autopilot?

Risk-based planning, workpapers, analytics, findings, follow-up, continuous monitoring and the committee pack, in one platform.